// Test Data Strategy & Management
// Test Data Is the Silent Quality Killer
Most teams either copy production data unmasked, a compliance risk, or hand-craft fixtures that never cover real edge cases.
Unmasked Production Copies
Real customer names, medical histories, and payment details sitting in test environments with no audit trail.
Data That Doesn't Cover Edge Cases
Production data rarely contains the boundary conditions and malformed inputs that actually break software.
Environments Waiting on Refreshes
Teams sit idle waiting for a manual data refresh instead of provisioning what they need on demand.
No Governance, No Accountability
No one can say who accessed what data, when, or whether it was ever supposed to be there.
A real test data strategy consulting engagement fixes the pipeline, not just one noncompliant dataset.
// The Frontier of Test Data Management Services
Synthetic data resolves the tension between realism and compliance, and it's what makes AI-driven QE possible.
Edge Case Generation
Synthetic test data services create scenarios real production data rarely contains: boundary values, malformed input, injection attempts.
Masking & Anonymization
When production data is used at all, irreversible masking replaces personal information while preserving statistical properties.
AI Training Data Quality
Validated for statistical balance, coverage, and bias, synthetic data increasingly doubles as AI training data.
AI Readiness Assessment
We evaluate your test data infrastructure for the programmability, volume, and traceability AI-driven QE requires.
// Compliance-as-Code, Not a Policy Document
Role-Based Access
//01Data stewards own access, engineers provision for their own tests, security audits, auditors get read-only visibility.
Audit Trails
//02Every provisioning request and data modification logged, with full version history for root-cause analysis.
Data Quality Monitoring
//03Freshness, completeness, and compliance status tracked in real time, with alerts on violations.
Compliance-as-Code
//04Non-compliant data simply can't be used, tests are blocked at the quality gate, not caught after the fact.
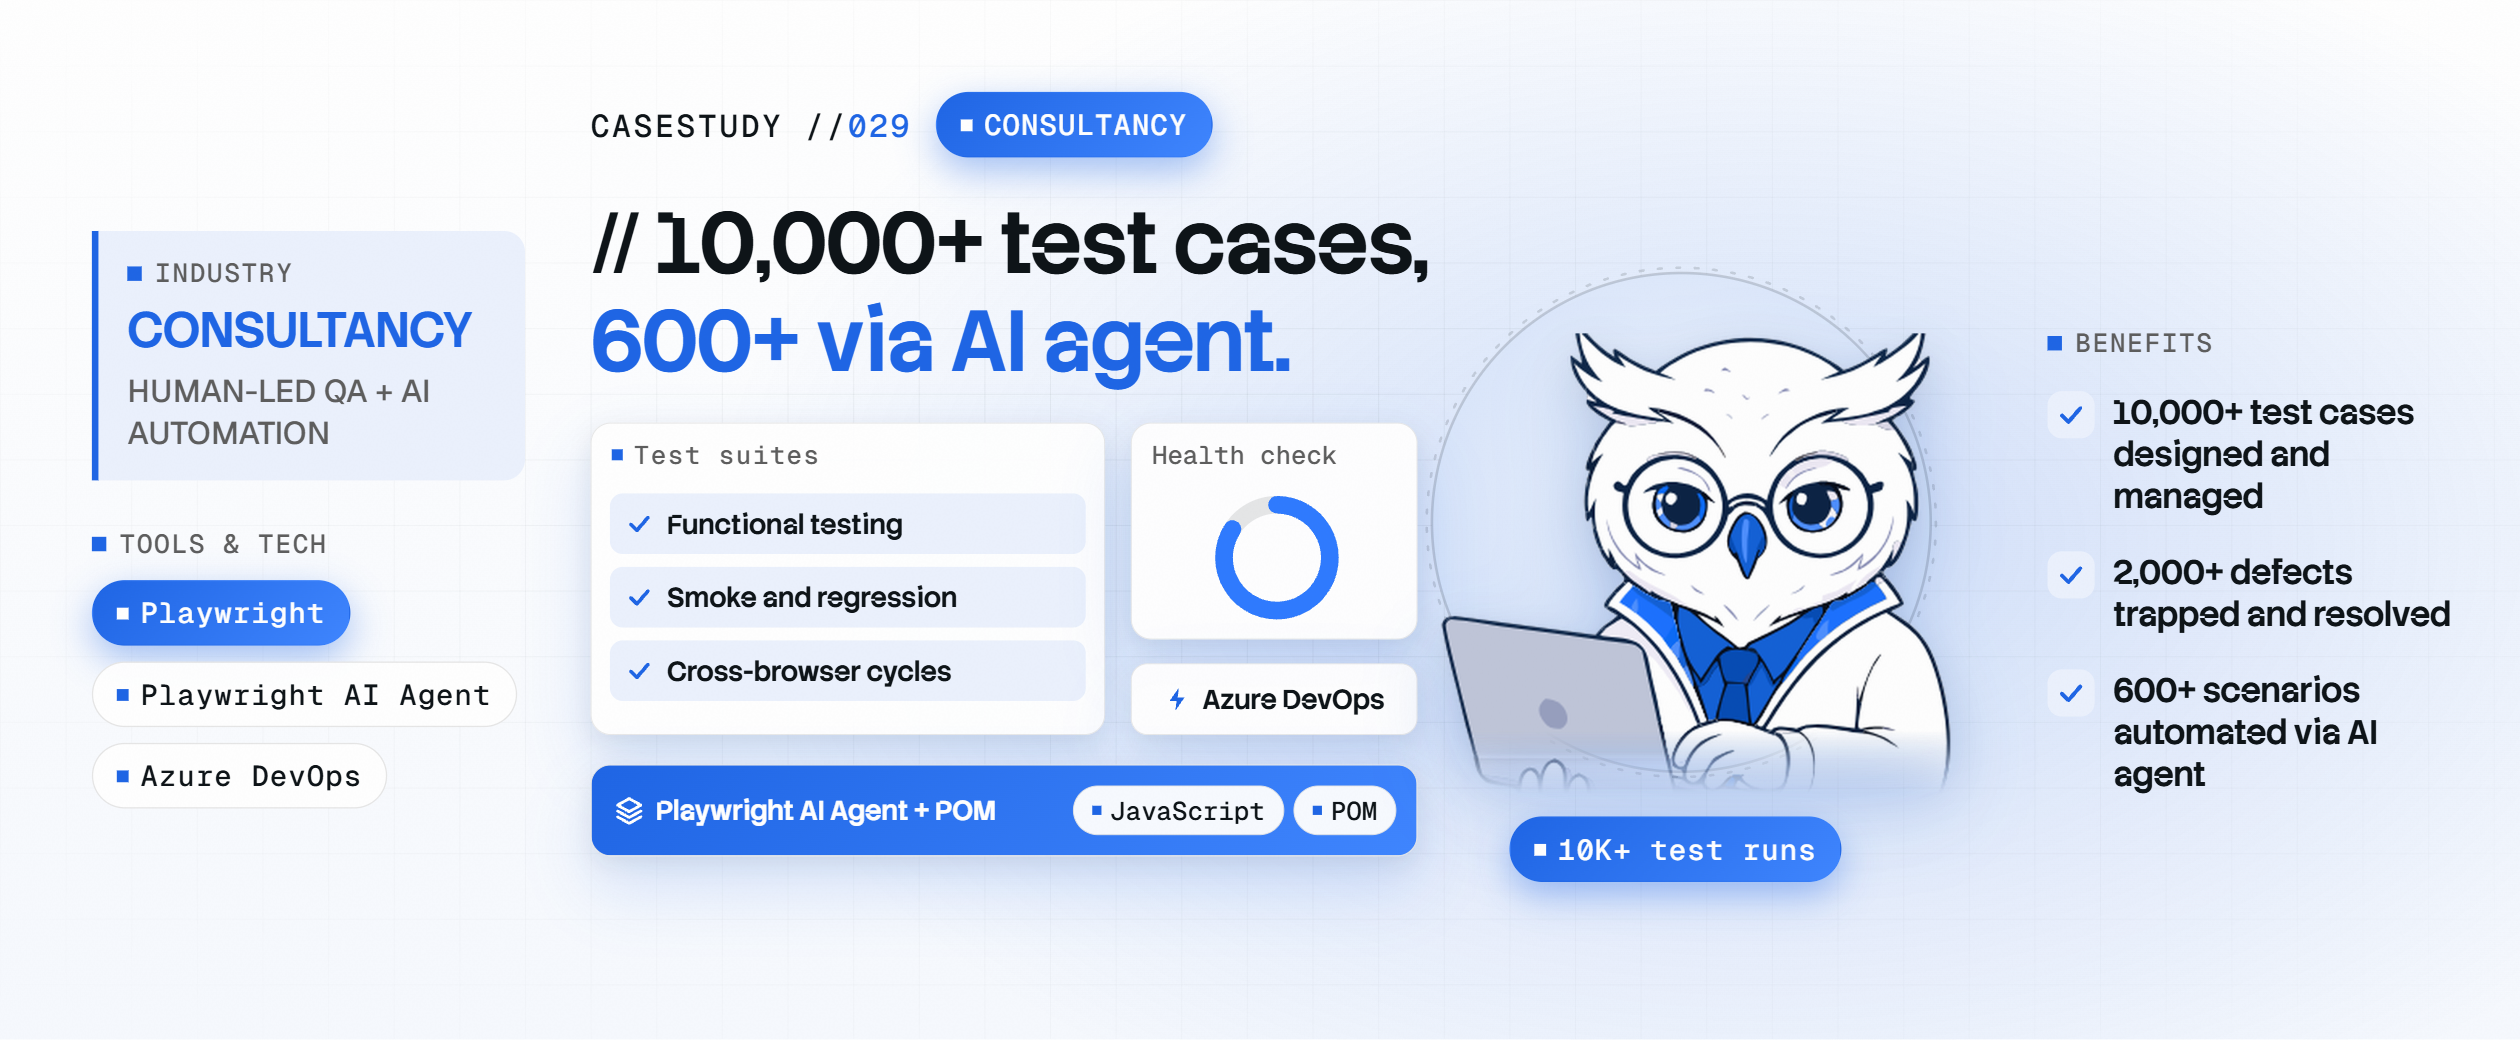
// Proven in the Real World.
// Test Data Provisioning Services,
at Your Scale
Test Data Assessment Only
An audit of current test data usage, compliance exposure, and provisioning bottlenecks.
Best For:Teams who need to know their exposure before committing to a fix.
Includes:Data usage audit, compliance gap report, prioritized recommendations.
// Where Test Data Fits in QE Consulting
// Latest Articles.
// Questions, Answered.
What is test data strategy and management?
The discipline of designing, generating, masking, and provisioning the data your tests actually run against, so testing is realistic, fast, and compliant, instead of relying on ad-hoc copies of production data.
Why not just use masked copies of production data?
Masking helps but doesn't solve everything, it can't generate edge cases production data never contains, and copying production at all carries risk. Synthetic data generates realistic edge cases with zero real personal data involved.
Does this help with GDPR, HIPAA, or PCI DSS compliance?
Yes. Synthetic and properly masked data removes real personal and payment information from test environments entirely, and compliance-as-code checks block tests from running against non-compliant data.
Can synthetic test data support AI model training?
Yes, when it's validated for statistical balance, coverage, and bias. Synthetic test data services increasingly double as AI training data services once that validation is in place.
How long does it take to move off unmasked production data?
A typical engagement runs 6-8 weeks: 1-2 weeks to audit current usage, 2 weeks to design the generator, and 4 weeks to build a provisioning service integrated with CI/CD.
Will this slow down our tests or reduce coverage?
Done well, the opposite happens. On-demand provisioning is typically faster than waiting for a data refresh, and synthetic generation can create edge cases production data never contains.
Who should own test data governance?
A data steward owns and approves access, test engineers provision for their own tests, security teams audit sensitive access, and auditors get read-only visibility, roles, not just a policy document.