// Autonomous Penetration Testing Services
// Why Traditional Pentests Create a False Sense of Security
Point-in-Time Blindspot
A pentest report from 3 months ago reflects an attack surface that's 3 months out of date. New APIs have shipped since.
Scope Limitations
Manual pentests sample-test endpoints. Autonomous scanning covers 100% of the declared attack surface continuously.
Fix-and-Forget Cycle
Vulnerabilities get found and ticketed, but rarely re-tested to confirm the fix didn't introduce a new regression.
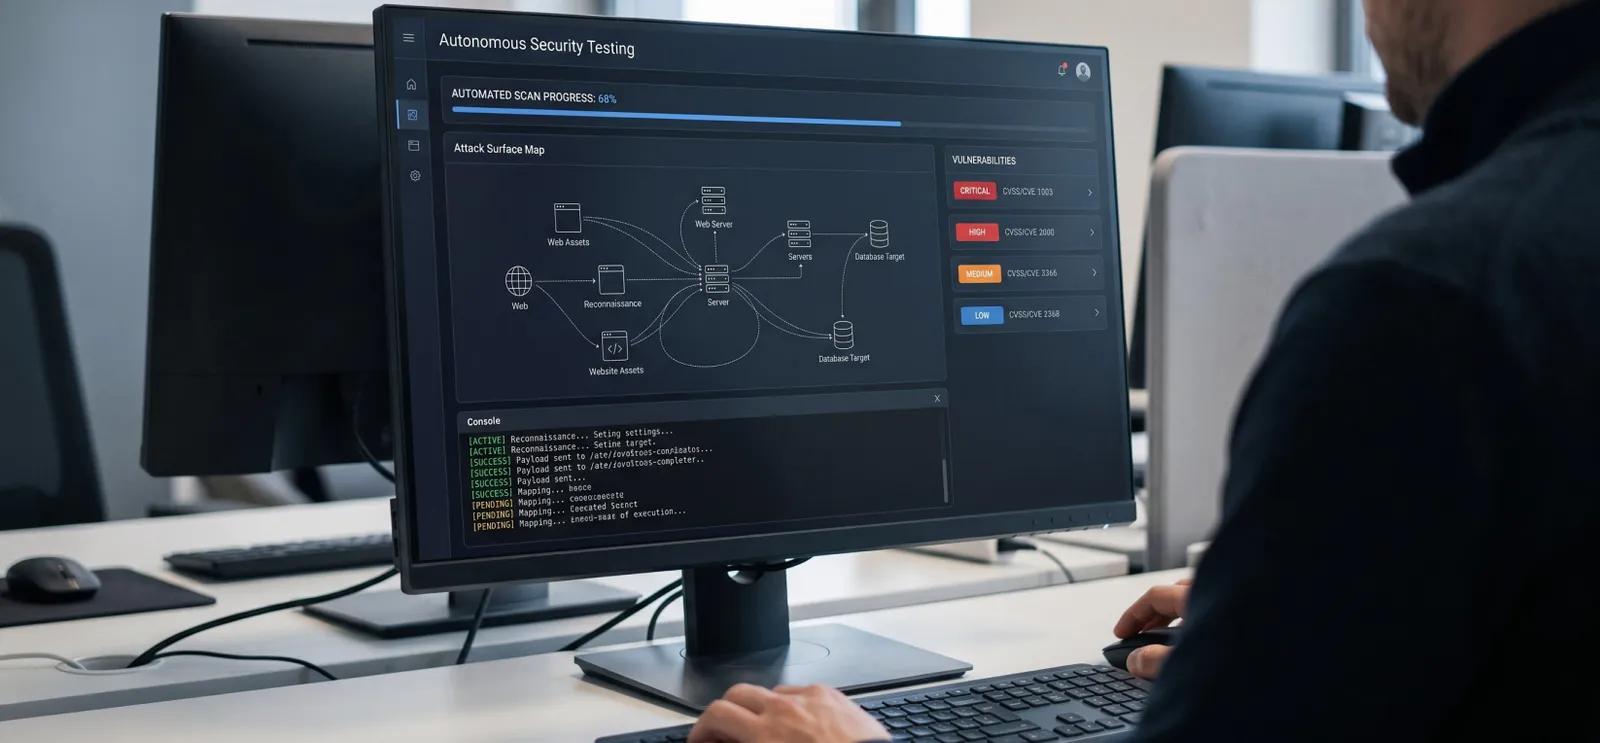
Our agentic pentesting services combine AI-driven scanning with expert-led manual testing that never stops.
// Jignect's Autonomous Pentesting Capabilities
AI-Augmented Attack Surface Discovery
Continuous mapping of exposed services, endpoints, and third-party integrations with AI-driven reconnaissance.
OWASP Top 10 Web & API Testing
Comprehensive scanning for injection, broken auth, broken access control, and sensitive data exposure.
Business Logic Vulnerability Testing
Expert-led testing for privilege escalation and abuse cases automated scanners are structurally unable to catch.
CI/CD-Integrated Security Gates
Continuous pentesting embedded in your build pipeline, with gates that fail on high-severity findings.
// Security Testing Tool Ecosystem
// Deliverables, Not Just a Findings List
CVSS-Scored Findings with PoC
Every finding scored and documented with proof-of-concept, ready for triage.
Executive & Technical Reports
Reports written for both your leadership and your engineers, not a single dense document.
Compliance-Mapped Findings
Every finding tied to OWASP, CVE, CWE, and NIST for direct use as audit evidence.
Re-test Verification
Every fix re-tested to confirm the vulnerability is actually closed, not just ticketed.
// Vulnerabilities Found Continuously. Not Quarterly.
// Latest Articles.
// Questions, Answered.
Who is Autonomous Penetration Testing built for?
It's built for teams relying on annual or quarterly pentests with months of blind exposure; teams shipping new APIs and features between scheduled test cycles; teams that fix vulnerabilities but rarely confirm the fix with a re-test; and teams needing findings mapped directly to SOC 2, PCI-DSS, or ISO 27001.
What's the difference between autonomous and traditional pentesting?
Traditional pentesting is a point-in-time engagement with a report at the end. Autonomous pentesting runs continuously, with AI-driven scanning finding new vulnerabilities and expert teams re-testing fixes and validating business logic in real time.
How do you avoid disrupting production during testing?
We schedule scanning windows with your team, tune tools to avoid state-changing requests, and run CI/CD-integrated tests in staging pipelines, all within your risk tolerance and operational constraints.
Do you test APIs and mobile apps as well as web apps?
Yes. REST, GraphQL, and gRPC APIs, iOS and Android apps, and backend services are all covered, mapped to OWASP with both automated scanning and expert-led manual validation.
How are findings reported and prioritized?
Findings are scored with CVSS 3.1, include proof-of-concept documentation and remediation guidance, and can integrate into your ticketing system, prioritized by severity, exploitability, and business impact.
Can you integrate pentesting into our CI/CD pipeline?
Yes. We integrate with GitHub Actions, GitLab CI, and Jenkins, with security gates that can fail builds on high-severity findings or run in advisory mode for shift-left feedback.
What compliance standards do your findings map to?
OWASP Top 10, CVE, CWE, and NIST, with compliance-ready reporting for SOC 2, PCI-DSS, ISO 27001, HIPAA, and GDPR that can be used directly as audit evidence.