// Quality Engineering Built For
The Stakes Of Healthcare.
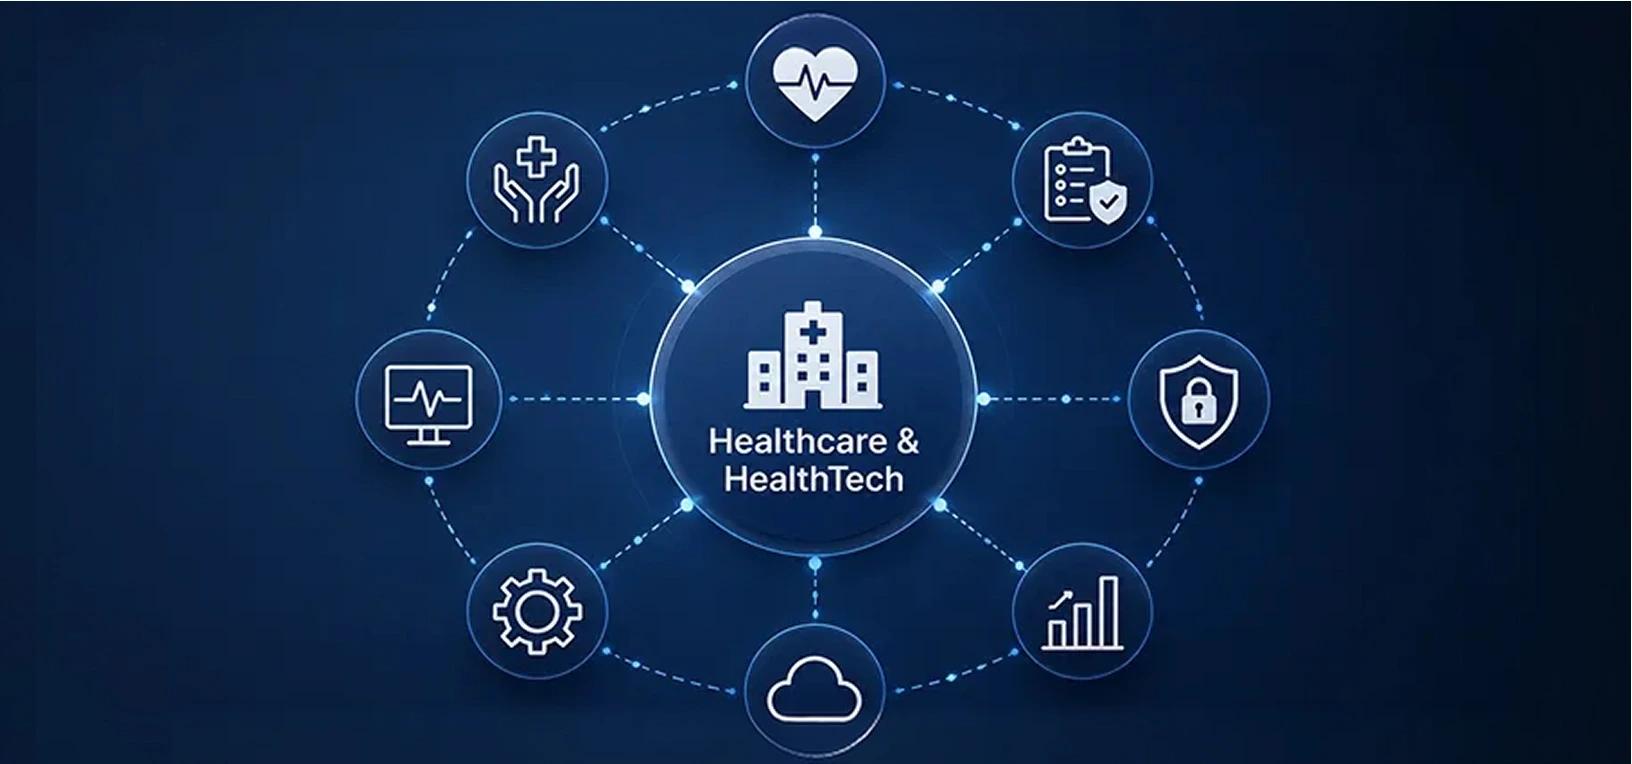
In healthcare, a software failure isn't a UX problem, it's a patient safety event. Jignect validates HIPAA, HL7, FHIR, and FDA 21 CFR compliance at every layer, so data integrity is never the defect nobody caught.
What We Test. What We Validate. What We Protect.
Eight domain-specific capability areas, each built around the clinical realities and regulatory obligations of the healthcare sector.
HIPAA Compliance Testing
//01Systematic validation of PHI handling across storage, transmission, and access control, aligned to HIPAA/HITECH and SOC 2 Type II controls, with audit log integrity and BAA verification.
HL7 & FHIR Integration Testing
//02Message-level validation of HL7 v2/v3 transactions (ADT, ORM, ORU) and FHIR R4/R5 APIs across EHRs, labs, pharmacies, and health information exchanges.
EHR & Clinical Platform Validation
//03Functional and regression testing for EHR modules: demographics, medication management, order entry, results routing. Epic, Cerner, Meditech.
FDA 21 CFR Part 11 Compliance
//04Validation documentation, e-signature integrity, and audit trails aligned to FDA requirements for computerized systems in regulated environments.
Telehealth & Remote Care QA
//05End-to-end testing of video session reliability, bandwidth degradation, device compatibility, and clinical workflows across patient and provider apps.
Medical Device Software (SaMD)
//06QE support for Software as a Medical Device: IEC 62304 alignment, traceability matrices, and post-market surveillance readiness.
Patient Portal & Accessibility
//07WCAG 2.1 AA validation for patient-facing portals, built for accessible experiences across older adults and patients with disabilities.
Healthcare Data Security Testing
//08OWASP-aligned security testing for clinical APIs, DICOM imaging systems, and PHI databases, including penetration testing and encryption verification.
// Systems & Platforms We Test.
EHR / EMR Systems
Telemedicine Platforms
Healthcare Mobile Apps
Billing & Insurance
Pharmacy & Lab Systems
Cloud-Based Healthcare Solutions
Hospital Management Systems (HMS)
Wearable & IoT Health Devices
AI-Powered Diagnostic Tools
Patient Engagement Platforms
// How Jignect Engages in Healthcare Environments
Regulatory Mapping
Before a single test is written, we map your regulatory obligations: HIPAA scope, FDA classification, FHIR conformance targets, agreed with your compliance team.
Risk-Based Test Strategy
Clinical risk drives test priority. We identify high-risk data flows, integration points, and patient-facing functionality for right-sized coverage.
Environment & Data Setup
Healthcare testing needs realistic, de-identified patient data. We implement synthetic data generation and PHI masking for compliant test environments.
Continuous Validation
Compliance isn't a one-time event. We embed validation checkpoints into CI/CD, catching regressions in FHIR APIs and PHI handling before release.
Audit-Ready Documentation
Every test cycle generates traceability artifacts: test plans, execution reports, and sign-off documentation aligned to your regulatory submission or audit.
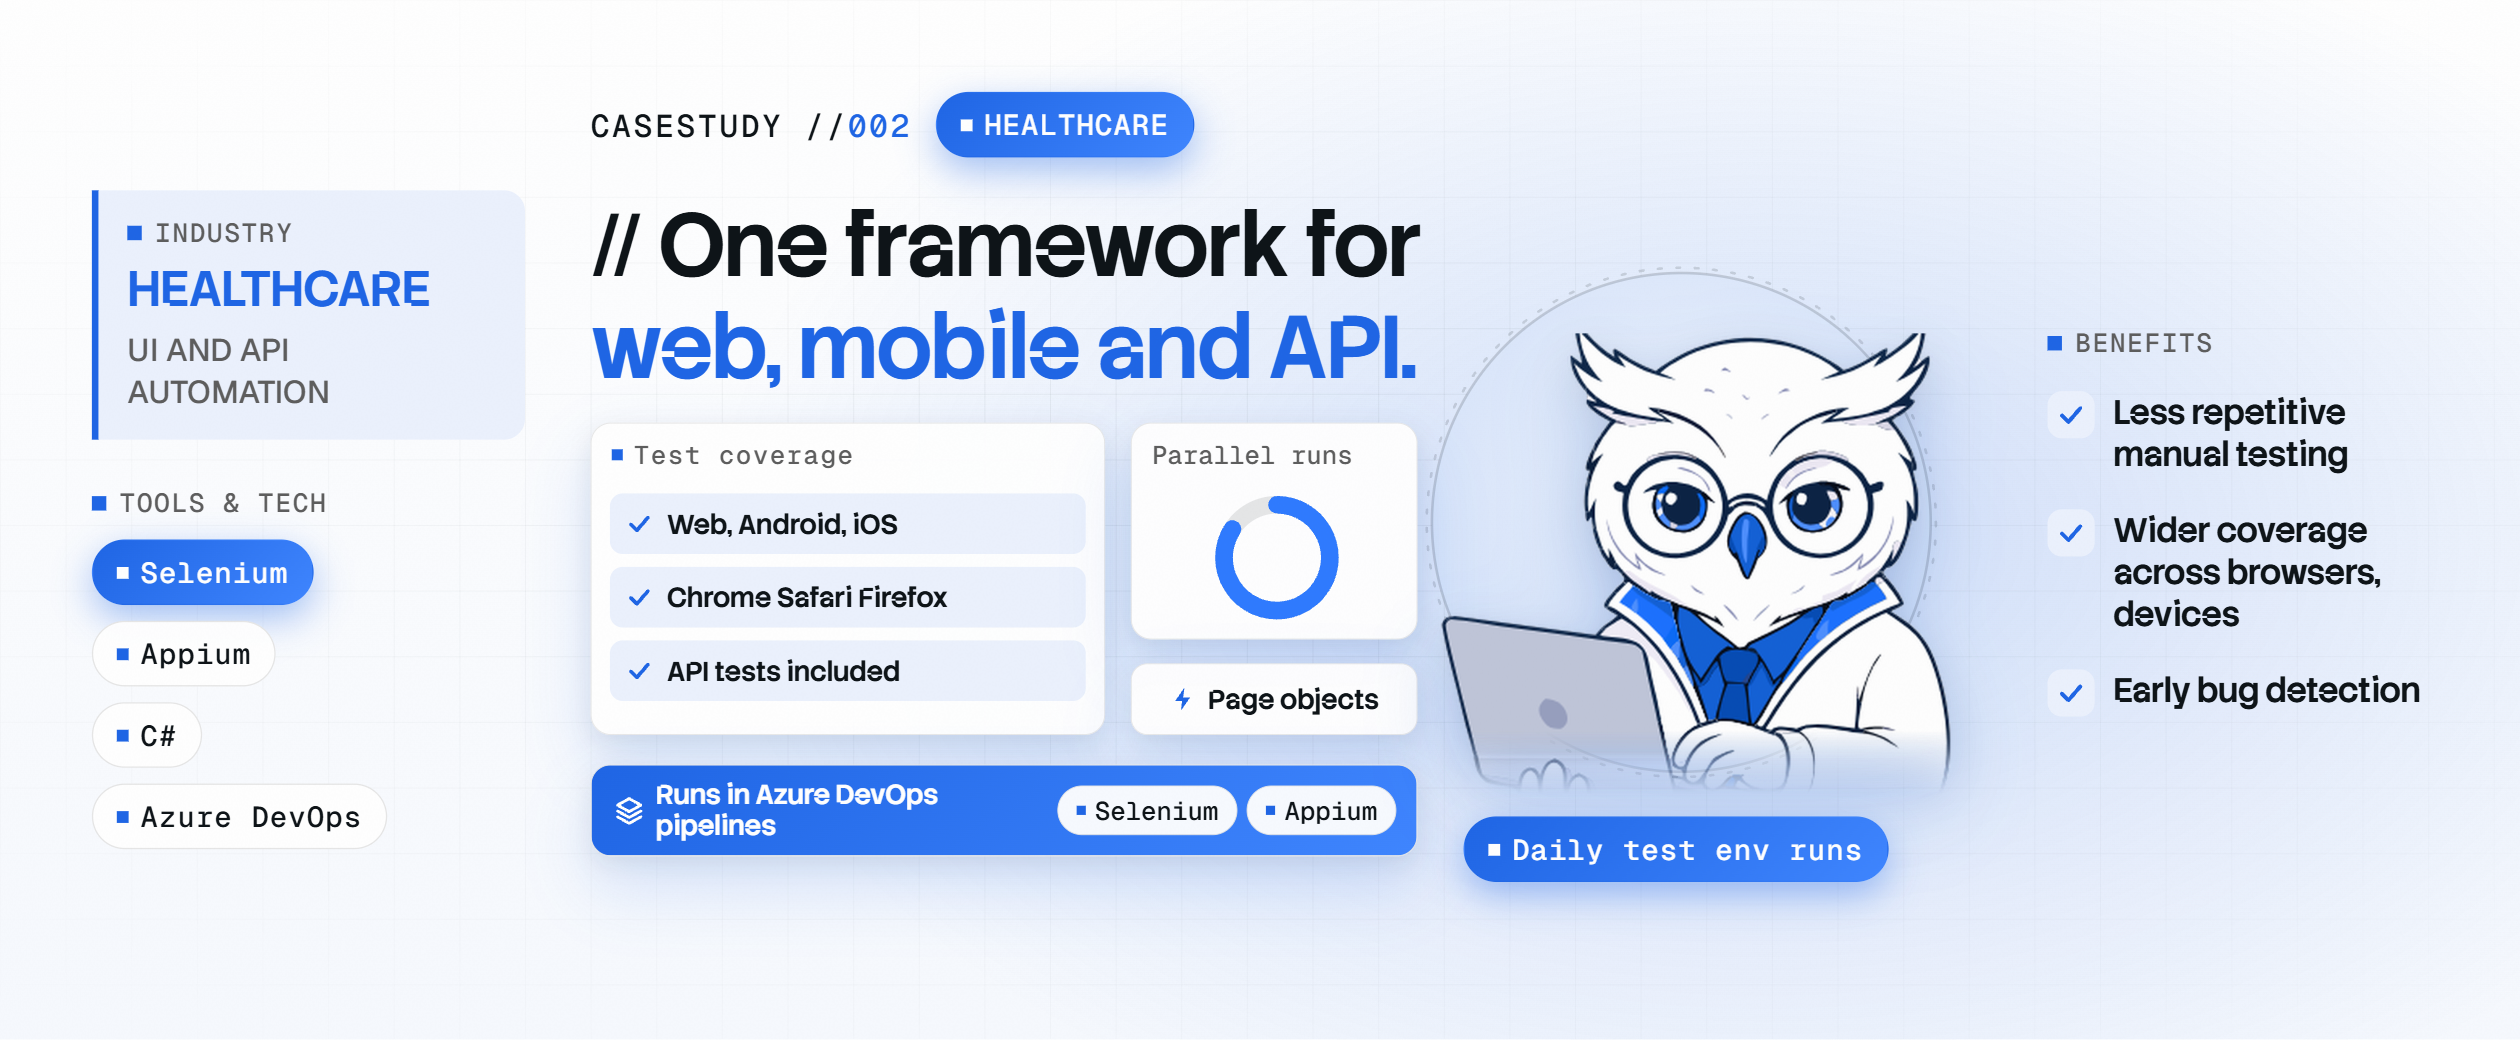
// From 3-Day Regression Bottleneck
to 4-Hour Automated Pipeline.
// What Engineering Teams SayAbout Working With Jignect.
// Questions, Answered.
Why does healthcare software need specialized QE instead of generic QA?
Generic QA checks that a feature works. Healthcare QE checks that it fails safely: a patient record mismatch is a liability, an EHR-to-lab interoperability gap breaks care coordination, and a missed vulnerability in a clinical API is a life-critical risk, not a support ticket.
Do your QE engineers have real healthcare domain experience?
Both. Our healthcare QE team includes engineers who have worked directly on clinical platform projects: EHR implementations, FHIR API builds, telehealth products. Domain knowledge isn't optional here, which is why clients treat us as their healthtech QA company for healthcare application testing services, not a generic QA vendor.
What regulatory frameworks and standards do you test against?
HIPAA/HITECH for PHI handling, HL7 v2/v3 and FHIR R4/R5 for interoperability, FDA 21 CFR Part 11 for electronic records, IEC 62304 for SaMD, ONC HTI-1 for information blocking, and SOC 2 Type II for platform security.
Can you help with validation documentation for FDA submissions?
Yes. We produce IQ/OQ/PQ documentation, traceability matrices, and test summary reports aligned to 21 CFR Part 11 and FDA software guidance.
How do you handle test data in HIPAA-regulated environments?
We use synthetic patient data generation and PHI de-identification pipelines. No real patient data is used unless the client already has compliant handling protocols in place.
Do you work with EHR platforms like Epic or Cerner?
Yes, our team has hands-on experience with Epic, Cerner, Meditech, and custom-built EHR and health information systems, adapted to your specific integration architecture.
Can you support FHIR API testing for ONC interoperability mandates?
Yes. FHIR R4/R5 API conformance testing is core, including resource validation, SMART on FHIR authorization, CDS Hooks, and ONC HTI-1 requirements.